
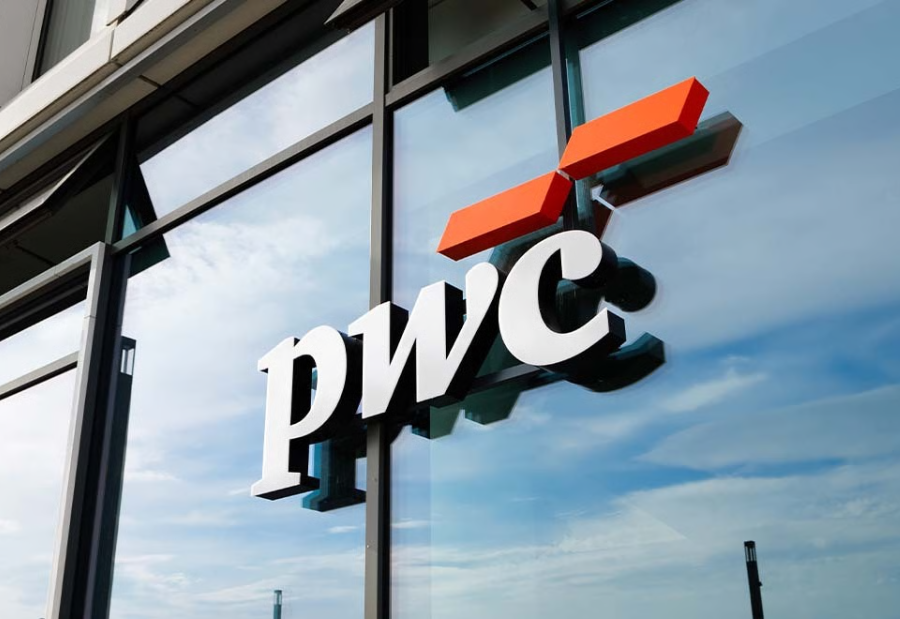
A cybersecurity incident involving an external service provider has drawn attention to the risks of storing employee information outside corporate networks. PricewaterhouseCoopers (PwC) confirmed the incident after the Everest cyber extortion group claimed it had stolen 590 GB of company data.
PwC acknowledged the incident on October 23, 2026, a day after Everest published its allegations. The affected third-party platform hosted employee learning records. PwC said it had secured the environment and started an investigation but did not verify the alleged data theft.
Everest claims access to employee information
Everest claimed the stolen material included “regional HR and learning exports, integration documentation, software components and PwC e-learning courses.”
The group also alleged that the data contained employee names, email addresses, phone numbers, physical addresses and employment histories. It posted a 5-day countdown on October 22, threatening to publish the information if an agreement was not reached.
These claims have not been independently verified. PwC has not confirmed the reported 590 GB volume or the specific categories of information allegedly obtained.
PwC says internal operations are unaffected
A company spokesperson said the affected platform did not contain client information, sensitive personal data or financial records.
“The affected site does not house client data, sensitive personal data or financial information. Once we learned of this incident we acted promptly to secure the environment and conduct a thorough review.”
The spokesperson added that the incident “does not impact our network or any of our operations.”
PwC has not disclosed the vendor’s identity, the number of potentially affected employees or how the external system was compromised. Its investigation was continuing as of October 26.
Everest’s previous cybercrime activity
The Everest group emerged in late 2020 and has operated as a cyber extortion group and initial access broker, according to cybersecurity researchers. It has reportedly offered cash payments and profit-sharing arrangements to recruit insiders.
The group has also claimed attacks involving critical infrastructure providers in several countries. In 2025, it claimed involvement in incidents affecting international airports through an attack on aerospace technology provider Collins Aerospace.
The PwC incident highlights the security risks associated with third-party platforms that handle employee records and internal business information. However, the company’s statements confirm an incident at an external provider, not a breach of its own network. The alleged theft and exposure of 590 GB of data remain unsubstantiated.
Also read: Viksit Workforce for a Viksit Bharat
Do Follow: The Mainstream LinkedIn | The Mainstream Facebook | The Mainstream Youtube | The Mainstream Twitter
About us:
The Mainstream is a premier platform delivering the latest updates and informed perspectives across the technology business and cyber landscape. Built on research-driven, thought leadership and original intellectual property, The Mainstream also curates summits & conferences that convene decision makers to explore how technology reshapes industries and leadership. With a growing presence in India and globally across the Middle East, Africa, ASEAN, the USA, the UK and Australia, The Mainstream carries a vision to bring the latest happenings and insights to 8.2 billion people and to place technology at the centre of conversation for leaders navigating the future.