
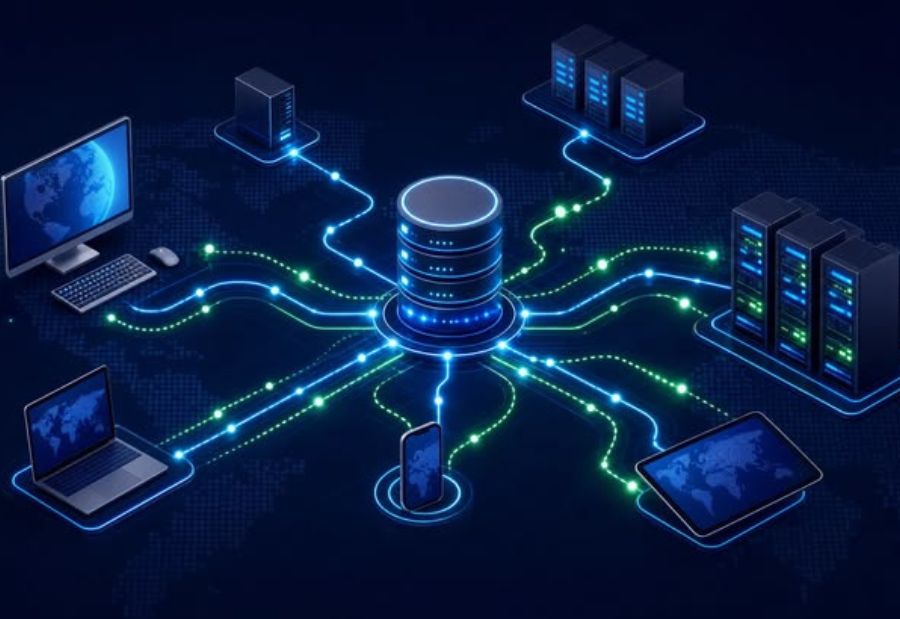
Organisations operating hybrid infrastructure rely on communication between on-premises data centres, private cloud environments, public cloud platforms and remote users. As these environments become more distributed, understanding how network traffic moves between systems becomes increasingly important.
Limited visibility can make it difficult to identify performance bottlenecks, investigate suspicious connections and understand application dependencies. Network teams may know that a service is experiencing delays without knowing whether the cause is congestion, routing, application behavior, or an external connection. Improving network traffic visibility in hybrid infrastructure helps organisations monitor communication patterns, identify unusual activity and maintain reliable connectivity.
What is network traffic visibility?
Network traffic visibility refers to the ability to observe, analyse and understand data moving across network environments.
It includes information about traffic sources, destinations, protocols, connection patterns, bandwidth usage and communication behaviour.
In hybrid infrastructure, visibility must extend across multiple environments rather than focusing only on an individual data centre or cloud platform.
For example, when an application hosted in a public cloud communicates with an on-premises database, IT teams should be able to understand the network path, traffic volume and performance of that connection.
Why is network traffic visibility important?
1. Faster performance troubleshooting
Visibility into network traffic helps teams identify latency, packet loss, congestion and routing issues.
Instead of investigating infrastructure components individually, teams can examine communication paths and narrow down the source of performance problems.
2. Better threat detection
Unexpected connections, unusual traffic volumes and communication with unknown destinations may indicate suspicious activity.
Traffic monitoring provides additional evidence that security teams can use during investigations.
3. Improved application dependency mapping
Modern applications often depend on multiple services, databases and external APIs.
Understanding these communication patterns helps teams identify dependencies and assess the potential impact of infrastructure changes.
4. More effective capacity planning
Traffic trends can reveal increasing bandwidth requirements and recurring periods of high network utilisation.
This information supports infrastructure planning and helps organisations avoid capacity shortages.
Key strategies for improving network traffic visibility
1. Centralise network monitoring data
Hybrid environments often use separate monitoring tools across cloud and on-premises infrastructure.
Centralising relevant network telemetry can provide a more complete view of traffic patterns.
Organisations should integrate supported data sources, including network devices, cloud network services, firewalls and application monitoring systems.
A centralised view can also make it easier to correlate network events across different environments.
2. Use network flow monitoring
Network flow records provide information about communication between network endpoints.
They commonly include source and destination addresses, ports, protocols, traffic volume and connection duration.
Flow monitoring can help teams identify high-volume connections, unexpected communication paths and potential network bottlenecks.
It is important to understand that flow records generally provide metadata rather than the full contents of network communications.
3. Implement network packet analysis where required
Packet analysis provides deeper visibility into network communication by examining packet-level information.
It can help investigate complex performance issues, protocol errors and suspicious network behaviour.
However, packet capture can generate large volumes of data and may involve sensitive information. Organisations should apply appropriate capture limits, access controls and retention policies.
4. Map application and network dependencies
Teams should understand how applications communicate with databases, APIs, cloud services and other infrastructure components.
Dependency mapping helps identify critical communication paths and potential single points of failure.
It also supports change planning by showing which services may be affected when a network route or infrastructure component is modified.
5. Monitor traffic across cloud and on-premises environments
Cloud-native monitoring tools may provide visibility into traffic within a specific cloud environment, but they may not cover every external network connection.
Organisations should combine relevant cloud telemetry with on-premises network monitoring.
This helps teams examine communication across the complete hybrid environment and identify gaps in monitoring coverage.
6. Establish baselines for normal network behavior
Network traffic patterns vary depending on applications, users, business hours and workload requirements.
Organisations should establish baselines for normal traffic volume, connection frequency and communication destinations.
Comparing current activity with these baselines can help identify unusual behaviour that requires investigation.
7. Integrate network and security monitoring
Network performance and security monitoring often examine the same communication data from different perspectives.
Integrating network telemetry with security monitoring platforms can help teams correlate suspicious connections with identity events, endpoint activity and cloud audit records.
This supports more informed investigations and reduces the need to analyse disconnected alerts.
Key metrics for network traffic visibility
| Metric | Monitoring Objective |
| Network throughput | Measure data transfer volume. |
| Bandwidth utilisation | Identify capacity usage. |
| Packet loss | Detect unsuccessful packet delivery. |
| Latency | Measure communication delays. |
| Connection frequency | Identify traffic pattern changes. |
| Traffic by destination | Understand where network data is moving. |
| Protocol distribution | Review the types of network communication. |
Final Thought
Network traffic visibility is essential for managing the complexity of hybrid infrastructure. Centralised monitoring, flow analysis, dependency mapping and consistent performance baselines can help technology teams understand how systems communicate across different environments.
For organisations managing distributed applications and cloud workloads, better visibility supports faster troubleshooting, stronger security investigations and more effective capacity planning.
The Mainstream explores network infrastructure and monitoring practices that help organisations improve technology performance and operational resilience.